
CONSULTING ON TISAX®: FAST AND WITHOUT HIDDEN COSTS
Consulting on TISAX® supports companies in the automotive supply chain from the GAP analysis and the build-up of the ISMS through to a passed assessment. Depending on the assessment level, the consulting costs from €18,000 (AL2) or from €24,000 (AL3) at a fixed price after scoping; a project takes 3 to 12 months. The consultant must not be the same as the audit provider – ENX rules this out.
Consulting on TISAX®: Our Experience
We help you accelerate your TISAX® project. Our consulting includes a joint GAP analysis, the preparation of the relevant documents and support during the audit.
Our team has worked in information security since 2019 and supports clients in obtaining the TISAX® label and confirming it in the re-assessment. More than 50 companies are happy to confirm our successful support.
Why Do I Need Consulting on TISAX®?
-
No hidden or additional costs, flat-rate price for your TISAX® label
-
Fair price structure depending on company size – from mid-sized supplier to OEM
-
Templates for ISMS, processes, TOMs and all necessary documents available
Templates for ISMS, processes, TOMs and all necessary documents available (in German)
-
Our consulting on TISAX® is aligned with your requirements – no one-size-fits-all approach
-
Our own e-learning platform for employee training and continuous awareness
Of course, not every company needs consulting on TISAX®. Perhaps you are an IT system house or an IT or information security service provider with experience in the topic who wants to assign a team to TISAX®. Then you may manage to obtain the label on your own, i.e. without consulting. If that is not the case, external help can accelerate your path to the TISAX® label, reduce costs and save a lot of time.
Below are some of the benefits of working with our competent consulting on TISAX®:
- Shorter overall project duration
- Avoidance of additional costs for re-audits
- A deeper understanding of the concepts and the motivation behind the TISAX® label
- Fewer delays on the way to the final label

How does a TISAX® project work?
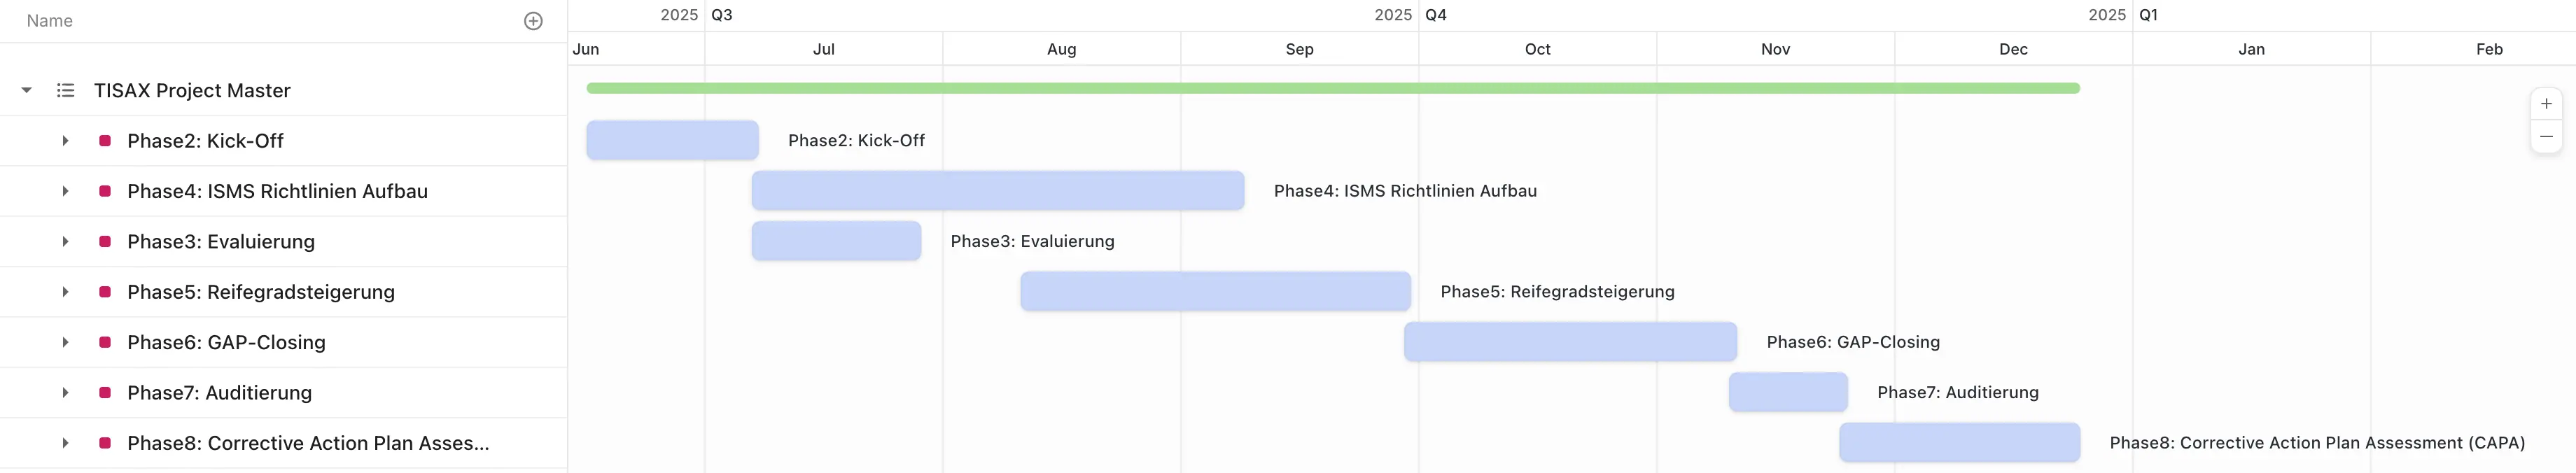
The project plan shows an example timeline, starting with phase 1, the gap analysis, through to the final audit and the resulting corrective action plan.
Are you ready to start your project?
Then our TISAX® GAP analysis is exactly right for you. At the end of the one-day GAP analysis, you receive your complete evaluation and the schedule for your TISAX® project: the roadmap to TISAX®.
Summary: TISAX® Costs and Time Required
Effort and duration depend mainly on the required assessment level, the assessment objectives (such as prototype protection or data protection), the number of sites and the maturity of your ISMS. As a rule, a TISAX® project takes 3 to 12 months; with an existing ISO 27001 certification it is usually faster. We work exclusively at a fixed price after scoping – the audit provider’s fees are not included and are invoiced directly by the audit provider.
| Service | Content | Price |
|---|---|---|
| GAP analysis | Maturity assessment, TISAX® roadmap (1 day) | €3,500 (up to 50 employees) / €4,500 (50 employees or more); for up to 50 employees, 50% is credited towards the follow-up project |
| Consulting on TISAX® – AL2 | ISMS build-up, self-assessment, documentation, assessment support | from €18,000 (fixed price after scoping) |
| Consulting on TISAX® – AL3 | As AL2, including preparation for the on-site assessment | from €24,000 (fixed price after scoping) |
| Scope extension | TISAX® scope extension for existing clients: transfer your existing TISAX® ISMS to a further site or a further company – as an extension instead of a new build-up, including ENX registration, self-assessment and assessment support. If the new company builds its own ISMS, this is a regular TISAX® project. | Quote after scoping |
| ENX registration | Mandatory fee to the ENX Association | €405 / site & scope, one-time per 3-year cycle |
| Assessment | External audit provider (depending on level) | As quoted by the audit provider (invoiced directly) |
You can find all cost factors in detail in our article on TISAX® costs (in German).
Your Path to Your TISAX® Label
- GAP analysis: We start with the GAP analysis and determine your maturity level.
- ENX registration
- Auditor selection: We can help you select and engage the audit provider.
- Audit preparation
- Building and implementing the ISMS
- Self-assessment
- TISAX® assessment: For AL2 it is usually carried out remotely (document review and interview via video conference), for AL3 on-site at your location.
We explain in detail what happens in each step in our article TISAX® requirements.
Step 1 determines the effort and cost of the entire project. Our scoping guide takes you through the ENX requirements in six steps — with a decision tree, site checklist and naming convention. Select the TISAX®-Scoping-Guide below.
The request form is in German — just select the guide and fill in name, company and e-mail.
What Costs and Duration Depend On

Costs and time required depend mainly on company size, the number of sites and the maturity of your ISMS.
TISAX® Labels and Their Benefits
- Higher security standards and transparency
- Trustworthiness for new customers through worldwide recognition of the label
- Relief for IT tasks, reduced effort and costs
- Easier day-to-day operations thanks to standardized processes
The TISAX® label confirms your security level and your quality standards, which are recognized by the largest manufacturers in the automotive industry. It provides a transparent and secure supply chain in line with the TISAX® requirements and helps all participants reduce their costs.
Consulting on TISAX®: From Zero to Label in the Automotive Industry
You have decided to obtain the TISAX® label. We offer you the GAP analysis at a fixed price. Based on the GAP analysis, we are happy to offer you an individual full package up to receipt of the label.
Our consulting on TISAX® is aimed at suppliers as well as engineering and IT service providers in the automotive industry whose customer (OEM or Tier 1) requires a TISAX® label – usually with assessment level 2 or 3. Typical starting points: you are preparing your first assessment and need clarity on scope, assessment objectives and sites. Your label expires after three years and the re-assessment is due – for assessments commissioned from January 1, 2027 on the basis of VDA ISA 2027. Your scope is changing due to new sites, prototype protection or data protection. Or you are already ISO 27001 certified and want to add the TISAX®-specific requirements in a targeted way. On request, we also advise internationally organized teams in English.
You receive support from a single source – from scoping to label.
- GAP analysis and scoping: Maturity level per control according to VDA ISA, definition of assessment level, assessment objectives and sites for ENX registration, action plan and fixed-price quote.
- ISMS build-up with proven templates: Information security policy, roles, asset and risk management, classification, security zones, supplier and emergency management – adapted to your processes instead of written from scratch.
- Implementation: Coordination with IT, HR, facility management and procurement, training and awareness for your employees, building up the evidence.
- Self-assessment and internal audit: We review your completed VDA ISA catalog before the assessment and close remaining gaps.
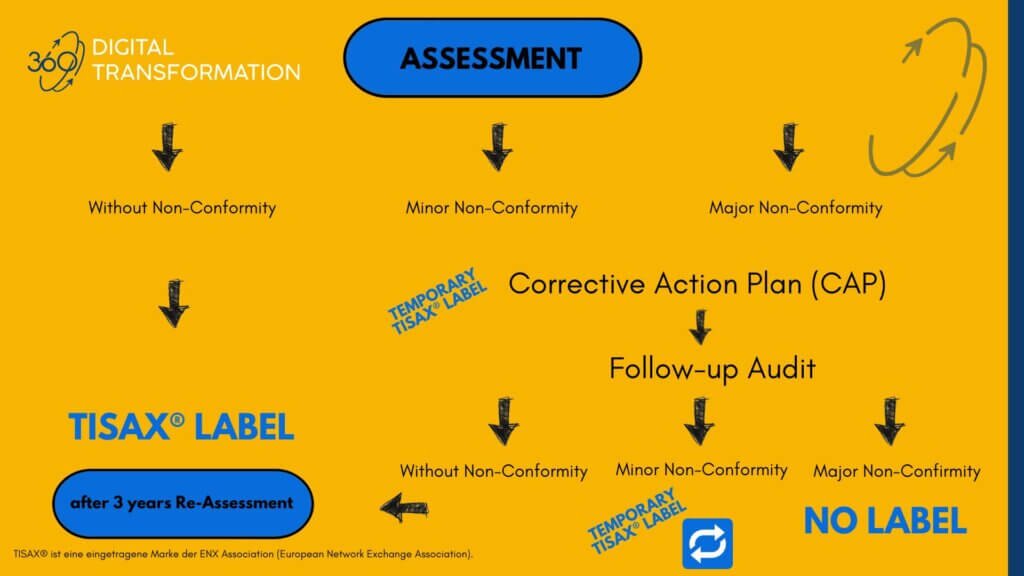
- Assessment and follow-up: Support in selecting the audit provider, support during the assessment and with the corrective action plan through to the label.
The assessment itself is carried out by an audit provider approved by ENX – 360DT advises but does not audit.
For the GAP analysis, a roughly defined scope (sites, targeted assessment level, any need for data protection or prototype protection) and insight into your existing QMS, IT security and ISMS documentation are sufficient. During the one-day workshop, the relevant contacts from IT, QM, information security and management should be available – that is all it takes to get started.
Our TISAX® Consultants


We Offer Two Ways in Which We Can Help You as Information Security Consultants
We help companies in the automotive industry and their partners achieve TISAX® efficiently, transparently and without detours.
Would you like to learn more about TISAX®? Do you have questions? You can schedule a free appointment.
Would you like to start your TISAX® project? Then you can book our GAP analysis to get your maturity level and the roadmap to TISAX®.
What Our Clients Say
The 360DT team not only advised us excellently, but was actively involved in the entire process and contributed significantly to our sites obtaining the TISAX® label.
For more than two years, the 360DT team has supported us as external information security officer and TISAX® consultant – competent, reliable and always on an equal footing. Thanks to the structured preparation, we successfully obtained the TISAX® label (AL3) with prototype protection and data protection.
From 0 to 100! In a very short time, the 360 Digitale Transformation team guided us to the TISAX® label in a highly professional manner.
Despite the tight schedule of our TISAX® project, 360DT supported us in an extremely responsive and practical way. Thanks to their expertise and commitment, we were able to complete the assessment smoothly and achieve excellent results.
Working with 360DT was very pleasant and on an equal footing, which prepared us optimally for the next steps and enabled us to complete the project successfully.
360 Digital Transformation has proven to be a reliable and competent partner in the implementation of our TISAX® Label AL3.

In 360DT, we have found a partner that operates in a highly professional and competent manner; it is technically and professionally proficient, meaning that measures and coordination with specialist departments such as IT, data protection, QMB, and management always took place on an equal footing, enabling us to implement the project successfully in a very targeted manner.

We had our server checked. We host many WordPress websites and wanted to be on the safe side. In fact, we were made aware of a few gaps. We were able to fix most of them ourselves. However, some were then fixed by 360DT. We now have an ongoing mandate to ensure long-term security. Thanks to Can and his team for the quick and, above all, instructive review of our server and hosting.
TISAX® from preparation to the label: pragmatic, objective, well-balanced, and timely implementation at an optimal price-performance ratio.

I felt perfectly supported throughout the entire process of obtaining our TISAX® label and look forward to continuing to work with 360 Digitale Transformation.
360 Digitale Transformation offers a clear plan without any beating around the bush. We felt that we received competent and targeted advice on the path to obtaining our TISAX® label.
What Is TISAX®?
Let’s start with the acronym. TISAX® stands for Trusted Information Security Assessment Exchange. Or, as it is known in the industry: ISO 27001 for automotive. It is often called “TISAX® certification” – formally, TISAX® is not a certification but a label, awarded after an assessment by an ENX-approved audit provider. It is based on the VDA ISA requirements catalog of the German Association of the Automotive Industry (VDA). TISAX® started on the basis of ISA 2.1; since 2019, the ENX Association has maintained the catalog. The catalog is continuously developed – ISA 6 currently applies; for assessments commissioned from January 1, 2027, ISA 2027, published on July 1, 2026, applies.

Before the TISAX® label, VDA members carried out assessments of their suppliers, partners and service providers in addition to their internal assessments. However, this individual assessment per supplier meant that partners had to spend time and money on the assessment by each of their customers.
To reduce the duplicated effort of similar assessments for different companies, the VDA developed its TISAX® requirements catalog. It contains the criteria by which audit providers assess information security; the result is shared with your customers via the ENX platform.
With a TISAX® label, a company demonstrates that its information security meets the required protection needs.
The VDA opted for a neutral third party, the ENX Association, which approves audit providers, maintains the assessment requirements, monitors audit quality and organizes the exchange of results.
What Are the Differences Between ISO 27001 and TISAX®?
In short: TISAX® is a label for the automotive supply chain with mandatory maturity levels and an assessment cycle every three years — ISO 27001 is the international certification standard with annual audits and a freely selectable scope. Which variant your customers really require and when the two can be combined is broken down in our detailed comparison TISAX® and ISO 27001: Differences and Similarities.
Would You Like to Learn More About the TISAX® Label?
Then take a look at our experts’ article on the TISAX® requirements. There we explain all the details of the TISAX® label.