
PENETRATION TESTING SERVICES FOR SMES: FAST AND VALUABLE
We have configured our penetration testing services specifically for SMEs. Do you want to test your information security and IT security? Do you need an expert analysis of your SaaS solution? Or is an audit according to ISO 27001, a TISAX® assessment or an IATF 16949 audit coming up? No problem – we are happy to help.
A penetration test (pentest) is an authorized, simulated attack on your IT. It is a security testing procedure designed to detect security vulnerabilities in computer systems, networks and web applications.
These security tests are carried out by “authorized” persons (so-called ethical hackers) to detect logic flaws and vulnerabilities in the specified information systems and to prevent malicious actors from exploiting these security gaps. Based on this, measures to raise the security level of the tested environments are proposed. The main purpose of a penetration test is to exploit the vulnerability in question and attempt to gain unauthorized access without damaging the system – not merely to detect vulnerabilities.
Penetration testing services: our experience
With our penetration tests, we help you understand the security level of your technical infrastructure, guide you through the process and provide you with a comprehensive report. In addition, we provide the necessary measures to eliminate the vulnerabilities uncovered by our ethical hackers.
Our team has been working in information security since 2019 – with a focus on network and web application pentesting. During this time, we have worked with a variety of clients throughout Germany. Our flexible, agile and client-oriented approach helps us deliver high-quality results.
Why do I need a penetration test?
A penetration test uncovers security vulnerabilities in your application, network or system. This allows you to fix them before attackers exploit these issues. There is no definition of a 100% secure system, and the techniques attackers can use to exploit a system are unlimited. The range of techniques varies depending on the attackers' experience with operating systems, software development skills and information systems. In addition, it is always a good choice to have the security vulnerabilities in your information systems reviewed by a third party.
Below are some of the benefits of working with our penetration testing services:
- increased information and IT security
- pentest report for your ISO 27001 or IATF certification or your TISAX® assessment
- prevention and/or minimization of damage from cyberattacks
- increased awareness among your employees
If you need detailed information about penetration tests, feel free to contact us.
Our advantages at a glance
- our pentesters work individually on your project to exploit the security vulnerabilities
- no hidden or additional costs, individual fixed prices for your pentests
- fair pricing depending on company and network size
- our pentests are aligned with your requirements – no one-size-fits-all approach
Want to learn more about our penetration testing services?
Or do you have questions about the penetration testing procedure? Then book a free, no-obligation appointment with us.
Penetration testing procedure
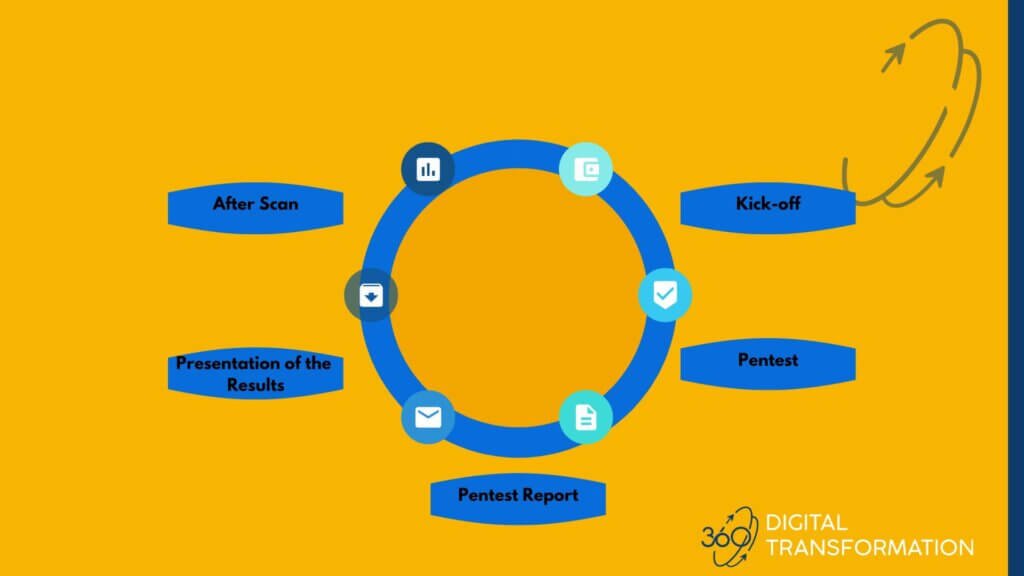
A typical penetration test consists of the steps listed below:
-
- Client meeting (gathering information and discussing the test conditions)
- Kick-off (scanning the test scope)
- Setting up VPN access from a German server to your in-house installation so that all scan results can remain on your infrastructure
- Vulnerability scan (scanning the networks provided by the client)
- Manual exploitation (identifying false positives, attempting to gain unauthorized access)
- Scenario execution (predefined scenarios with or without prior knowledge of the systems)
- Pentest report (including the vulnerabilities discovered and measures against them)
- Final meeting (presentation of the test report and recommendations)
- Follow-up check of whether the implemented measures were sufficient (if required)
What do the penetration testing services cost?
Naturally, the cost of penetration tests varies from company to company. However, we have summarized the available options with the corresponding price ranges. The cost of penetration tests is mainly influenced by two factors, explained in detail below:
- Size and complexity of your network and company: the effort depends on the number of network components, servers, locations, etc.
- Test duration and method: black box, white box or gray box? Perhaps we want to take a “time-boxed” approach. Your exact requirements define the test duration and therefore the cost.
Overall, our penetration tests start from €3,600 (fixed price after scoping). If you consider the effort involved in a cyberattack, a penetration test pays for itself as soon as it prevents a single successful attack.
Two ways we can help you
We are here so that you can get your pentest result at lower cost and faster.
Do you have questions about penetration tests? Then book a free appointment.
Ready to start your penetration tests? Then book our vulnerability scan so that you know your security gaps and can define the next steps.
International norms and standards



What types of penetration tests are there?
Network penetration test
If the penetration test focuses on your network, it is a network penetration test. Firewalls, servers, WLANs, VLANs and VPN access points are tested for security gaps and vulnerabilities.
The network infrastructure on premises and in the cloud, such as virtual system hosts, routers and switches, is assessed. A pentest can be carried out either as an internal penetration test, which focuses on resources within the corporate network, or as an external penetration test, which also targets the corporate network infrastructure reachable via the internet. To plan a test, you need to know the number of internal and external IPs to be tested and the size of the subnet.
Web application penetration test
This is a comprehensive assessment of websites and custom applications provided specifically over the internet, uncovering coding and development errors that could be exploited maliciously. Before starting a web pentest, it is essential to clarify how many applications need to be tested, including the number of static pages, dynamic pages and input fields to be checked.
Mobile application testing
A mobile application pentest checks iOS and Android apps for vulnerabilities in authentication, authorization, data storage and session management. To carry out a pentest, the testers need to know both the operating system types and the versions. The testers can also use them to test an application and find out the number of API calls and jailbreak requirements.
€211 billion
minimum damage to German companies from data theft, espionage and sabotage in 2026¹
58%
of companies suffered damage from cyberattacks in the past twelve months¹
119
new vulnerabilities in software products per day²
950
ransomware attacks in Germany, 80% of them on small and medium-sized companies²
*Sources: ¹ Bitkom, Wirtschaftsschutz 2026 (August 2026) · ² BSI, Die Lage der IT-Sicherheit in Deutschland 2025 (November 2025, reporting period July 2024 – June 2025).
Social engineering/phishing and pentests?
Social engineering is one of the many possible ways for hackers to get into your environment. Although companies invest a lot of money in security hardware and software, employees are the weakest link in the chain. Hackers know this very well! Since hackers also have plenty of time, they research employees' social media accounts and try to craft an e-mail that persuades them to click the link in the e-mail or download the attachment. Of course, the link or file is malicious and could give the hacker a way into your systems.
Sending deceptively genuine e-mails with malicious links or attachments is called phishing. With a phishing simulation (in German), we test how your employees react – without real malware. Social engineering attacks, on the other hand, are personalized, and hackers need a lot of time.
Want to learn more about penetration tests?
Then take a look at our blog post Penetration Testing: All You Need to Know, in which we explain penetration testing services in detail. Or check our FAQ. Still have unanswered questions? Then book an appointment with us.
Frequently asked questions:
What are the technical requirements for a pentest?
To set up secure access, we need VPN access, a VM that can reach all subnets, and an AD user for identity and access management checks.
How long does a penetration test take?
It depends on your network size and requirements. A penetration test can take between one and three weeks.
How much does a penetration test cost?
It naturally depends on the complexity of the project. Costs start from €3,600 (fixed price after scoping). If you need more information about penetration test costs, request a quote directly.
Which tools do you use?
We use a combination of open-source Kali Linux and licensed Tenable Nessus (or Greenbone) to carry out our penetration tests.
You do not pay any license costs – our tooling is included in the quote.
Do you carry out a retest?
Depending on your requirements and test objective, we offer the option of a retest.