
ISO 27001 CONSULTING FOR SMEs
ISO 27001 consulting for SMEs supports companies in setting up an information security management system (ISMS) in accordance with DIN EN ISO/IEC 27001. Our experienced consultants guide you from the GAP analysis and the creation of the necessary policies through to preparation for internal and external audits. With practical consulting, we ensure that your company meets the requirements of the international standard and that information security is permanently and verifiably ensured.
Our experience as ISO 27001 consultants
Our consultants guide you through a joint GAP analysis, the preparation of the relevant documents and support during the audit.
Working in information security since 2019, we have successfully supported numerous clients in preparing for and completing ISO 27001 certification and recertification. More than 50 satisfied clients can confirm this.
ISO 27001 specialists from 360 DIGITALE TRANSFORMATION
Every certification audit we have supported has been passed. Behind this 100% pass rate are long-standing experience, consistent commitment and sound expertise.
Our consultants keep their knowledge up to date through continuous professional development and extensive additional qualifications.
Our specialists are qualified as ISO 27001 Lead Implementers and Lead Auditors and certified by recognized training and certification providers.
In addition, 360 DIGITALE TRANSFORMATION has itself been certified to ISO/IEC 27001:2022 since July 2025 and thus meets the highest requirements for information security and compliance. We help you implement your ISO 27001 certification smoothly.
Our advantages as senior information security consultants at a glance
We know the path from both perspectives: we built our own ISMS and had it certified. In addition:
- There are no hidden or additional fees. We support you at a fixed price through to ISO 27001 certification.
- Fair pricing depending on company size.
- Templates available for the ISMS, processes and all necessary documents.
- Our ISO 27001 consulting for companies is fully tailored to your individual requirements.
- We help you find the optimal, independent certification body for you.
- Our own e-learning platform for training your employees and for ongoing awareness building.
The services of our ISO 27001 consulting
The services of our ISO 27001 consultants include advice and support in implementing an ISMS – information security management system in accordance with ISO 27001 – as well as preparation for the certification audit. We follow the DIN ISO 27001 standard, which governs risk management and security measures for an information security management system.
Our competent consultants support you in creating and implementing an ISO 27001-compliant ISMS. They accompany you in conducting internal audits and in dealing with deviations from the ISO 27001 standard.
Our consulting covers both the information security officer (ISO) role and the management system itself. The goal is to complete your ISO 27001 certification successfully and thus ensure information security in accordance with ISO 27001.
After certification, we can take over operation of the ISMS through an external CISO on request.
Why is ISO 27001 consulting worthwhile?
Of course, not every company needs ISO 27001 consulting to obtain its certification. Most do, however! With an expert on board, you can reduce the resources and time you spend on certification and thus lower your costs.
Below are some of the advantages of working with our ISO 27001 consulting service:
- Reduction of the overall project duration
- Avoidance of additional costs for repeat audits
- A more thorough understanding of the concepts and the motivation behind certification
The project duration can be between 3 and 9 months. And please do not forget that you also need to budget for the costs of the independent certification body.
Are you ready to start your ISO 27001 project?
Then our ISO 27001 GAP analysis is the right choice for you. At the end of the 1-day workshop, you receive your complete GAP analysis as well as the schedule for your ISO 27001 project: the ISO 27001 roadmap.
If your customers are based in the USA, ISO 27001 alone is often not enough: there, the SOC 2 report is required. The two standards overlap strongly – learn more on our SOC 2 consulting page.
How is an ISMS according to ISO 27001 structured?
An ISMS (information security management system) according to ISO 27001 is structured in line with the requirements of the standard and comprises the creation and implementation of policies, procedures, processes and technologies to ensure information security. Employee training is an important part of the ISMS, so that staff acquire the necessary expertise in data security.
As responsible management, you must ensure that the requirements of the ISO standard are met in order to guarantee the confidential processing of information. To implement these requirements, you can draw on consulting on the management system according to ISO 27001.
The ISO 27001 certification audit is carried out by an accredited certification body and checks whether the information security management system meets the requirements of the ISO standard.
An ISMS also gives companies the opportunity to qualify for participation in TISAX® (Trusted Information Security Assessment Exchange), an exchange of information security information between automotive manufacturers and their suppliers. The ISMS ensures that information security is managed effectively and that the requirements of the standard are met.
If you use or deliver AI, you build the next management system on the same foundation: our ISO 42001 consulting (in German) shows how an AI management system builds on your existing ISMS and supports implementation of the EU AI Act.
The process for ISO 27001 certification
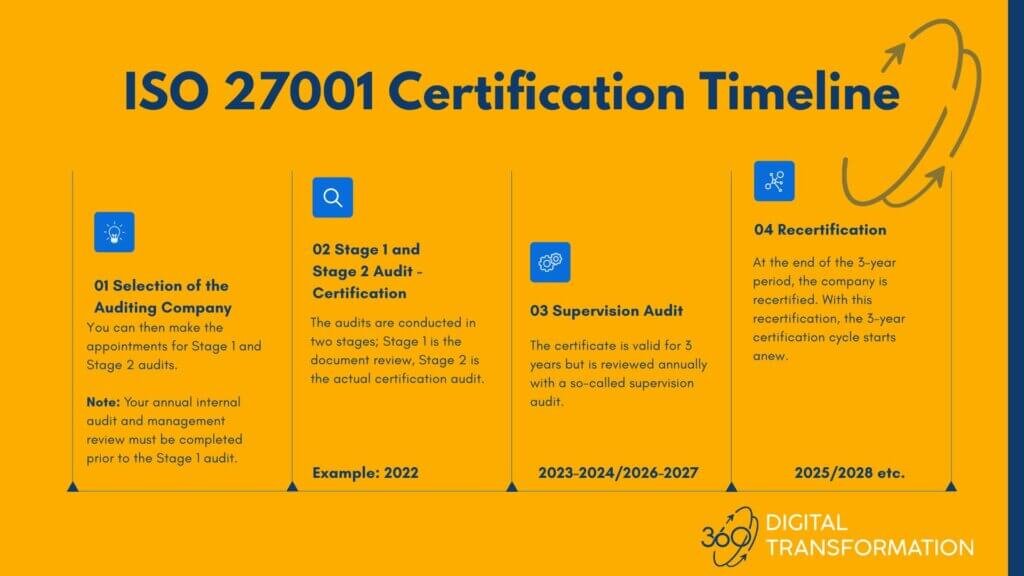
You might also be interested in: ISO 27001 certification in 7 steps (in German).
ISO 27001 certification and its benefits
- Higher security standards and transparency
- Trustworthiness for new customers thanks to the globally recognized certificate
- Relief for IT tasks, reduced effort and costs
- Easier day-to-day operations through standardized processes
ISO 27001 certification confirms your level of security!
Two ways we can help you
We are here so that you can obtain your ISO 27001 certification with lower costs and less time.
Would you like to learn more about the management system according to ISO 27001, or do you have questions? Then book a free appointment.
Do you already want to start your ISO 27001 project? Then book our GAP analysis so that you have access to your maturity level and your ISO 27001 roadmap.
Our consultants support you in implementing an ISMS according to ISO 27001


Customer reviews of 360 DIGITALE TRANSFORMATION
Our goal is for every client to recommend us. Here are some reviews from our clients.
The 360DT team not only advised us excellently, but was actively involved in the entire process and contributed significantly to our sites obtaining the TISAX® label.
For more than two years, the 360DT team has supported us as external information security officer and TISAX® consultant – competent, reliable and always on an equal footing. Thanks to the structured preparation, we successfully obtained the TISAX® label (AL3) with prototype protection and data protection.
From 0 to 100! In a very short time, the 360 Digitale Transformation team guided us to the TISAX® label in a highly professional manner.
Despite the tight schedule of our TISAX® project, 360DT supported us in an extremely responsive and practical way. Thanks to their expertise and commitment, we were able to complete the assessment smoothly and achieve excellent results.
Working with 360DT was very pleasant and on an equal footing, which prepared us optimally for the next steps and enabled us to complete the project successfully.
360 Digital Transformation has proven to be a reliable and competent partner in the implementation of our TISAX® Label AL3.

In 360DT, we have found a partner that operates in a highly professional and competent manner; it is technically and professionally proficient, meaning that measures and coordination with specialist departments such as IT, data protection, QMB, and management always took place on an equal footing, enabling us to implement the project successfully in a very targeted manner.

We had our server checked. We host many WordPress websites and wanted to be on the safe side. In fact, we were made aware of a few gaps. We were able to fix most of them ourselves. However, some were then fixed by 360DT. We now have an ongoing mandate to ensure long-term security. Thanks to Can and his team for the quick and, above all, instructive review of our server and hosting.
TISAX® from preparation to the label: pragmatic, objective, well-balanced, and timely implementation at an optimal price-performance ratio.

I felt perfectly supported throughout the entire process of obtaining our TISAX® label and look forward to continuing to work with 360 Digitale Transformation.
360 Digitale Transformation offers a clear plan without any beating around the bush. We felt that we received competent and targeted advice on the path to obtaining our TISAX® label.
Frequently asked questions about information security according to ISO 27001
What are the prerequisites for ISO 27001 certification?
An established ISMS, operational ISO 27001 processes and KPIs are the milestones on the way to ISO 27001 certification. An existing ISO 9001 certificate, however, simplifies the path to ISO 27001 certification.
Who audits ISO 27001?
The certification audit according to ISO 27001 is carried out by an auditor from an independent certification body. The prerequisite is that the certification body is accredited for ISO/IEC 27001 (in Germany by DAkkS). The certification company must be commissioned independently. We can help you with the selection and commissioning.
Who certifies according to ISO 27001?
In every country, there are certain institutions that act as the supervisory authority for ISO certifications such as ISO 9001, ISO 14001, ISO 27001 etc. In Germany, for example, the accreditation body is called DAkkS (Deutsche Akkreditierungsstelle, the German accreditation body). DAkkS is the national accreditation authority of the Federal Republic of Germany. DAkkS accredits certification bodies nationwide.
Other accreditation bodies include UKAS (United Kingdom) and IAS (USA). They are united in the International Accreditation Forum (IAF), which governs mutual recognition.
Note: Please ask your certification body about its accreditation and its accreditation certificate.
How much does ISO 27001 cost?
That naturally depends on the maturity of your company. The project duration is 3–9 months; consulting costs from €20,000 (fixed price after scoping). We have described a detailed breakdown of the costs of ISO 27001 certification in this article.
What are the criteria for selecting an ISO 27001 certification company?
The certification body must be accredited for ISO/IEC 27001 – by DAkkS or another accreditation body that is a member of the IAF MLA. We help you find an independent certification body.
How much time does a company need to plan for information security according to ISO 27001?
The time required depends on the size of your company. Of course, it also depends on the maturity of your information security management system. The total project duration is between 3 and 9 months.