
Your company has now decided to obtain a TISAX® label. Perhaps you are even required to go through a TISAX® assessment.
Either way: welcome to the club! TISAX® is a very extensive topic, so if you are new to TISAX®, I would recommend starting with the TISAX® requirements at a glance.
In this post, after covering some basics, we will focus on performing a self-assessment for TISAX®. This blog post is therefore aimed at companies that are already further along in their TISAX® process – for example, companies that have already decided on a TISAX® assessment or need to obtain the TISAX® label as quickly as possible.
What does a typical roadmap for TISAX® look like?
This question comes up very often, so we would like to start with the roadmap for TISAX®. Once you have decided on a TISAX® assessment, you should start by registering on the ENX TISAX® portal.
According to the ENX price list, the registration fee is €405 per location and scope (as of October 2026). After registration you will receive your SCOPE ID. Congratulations – you have successfully completed the first step towards your TISAX® label. 👏
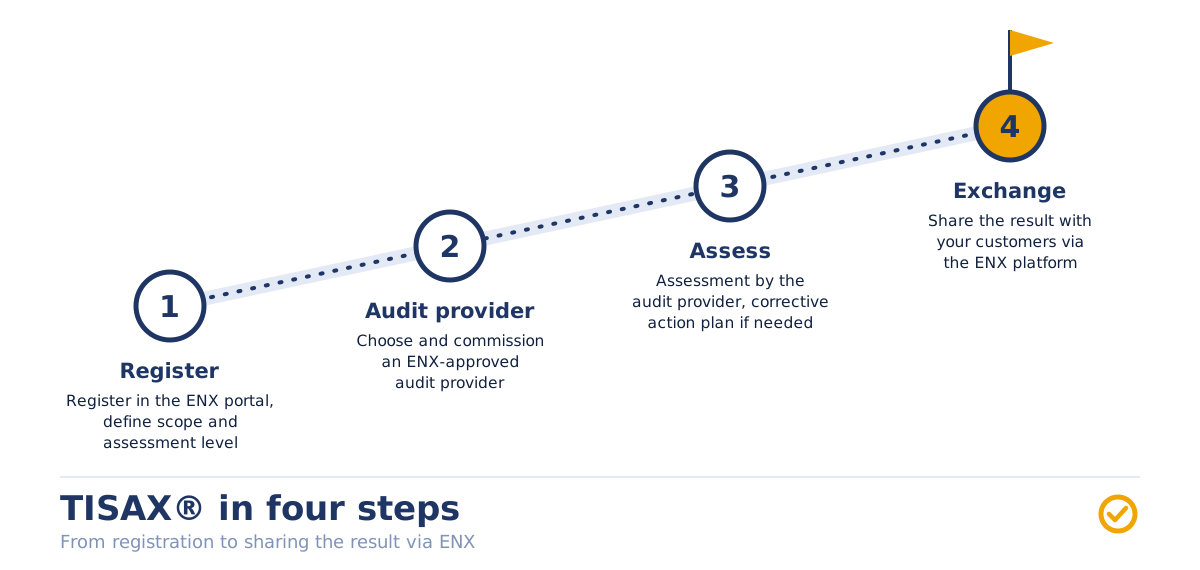
TISAX® assessment stages
After this step, you need to choose the audit provider. However, we strongly recommend completing your preparations before you decide on an assessment date. Why? If you are not sure how ready you are for your assessment, you are doing two things. First, you are putting yourself under time pressure. Second, by skipping the preparation you are jeopardizing a smooth assessment. So: preparation first!
You choose your audit provider from the list of companies approved by ENX. Examples of such companies are DEKRA, TÜV, KPMG, etc. You can obtain offers from different audit providers and then decide which one suits you best. After your decision, the audit provider will ask you to agree on an assessment date and a kick-off meeting. We recommend planning enough time between the kick-off meeting and the audit.
How do you prepare for your TISAX® assessment?
You need to do your homework before setting the audit date. The preparation time depends on the ISMS maturity of your company. We recommend allowing sufficient time for preparation, so avoid rushing into the audit. Let's dive into the preparation steps.
A GAP analysis is like an X-ray for doctors. It determines the maturity level of your company. It also shows in which areas your company needs to improve in order to obtain the TISAX® label. This is what a GAP analysis covers:
- Physical security questionnaire
- ISMS structure
- Technical security
- Self-assessment
In this blog post you will receive detailed information about the self-assessment for TISAX®, so we will only cover this aspect of the GAP analysis. The result of the GAP analysis is influenced by your ISMS structure, your document management system (DMS), your documentation policies, your security policies, your network plan, etc.
TISAX® requires a certain structure and clearly defined policies. It is therefore crucial that these are already in place. If that is not yet possible, performing a self-assessment for TISAX® will help you find out in which areas your company needs more preparation – and which requirements are a must.
What are the components of the self-assessment for TISAX®?
You carry out the self-assessment for TISAX® using the VDA ISA catalogue (Information Security Assessment) of the German Association of the Automotive Industry (VDA). The catalogue consists of questions on information security, prototype protection and data protection. Please note, however, that not all three areas are relevant for all TISAX® assessment levels.
The self-assessment is also provided as audit documentation, so it is important to carry it out thoroughly. We recommend performing the self-assessment twice: once before the project starts as a baseline, and once before the assessment as the final version. This way, the final version of the self-assessment can be produced without additional effort.
Cover page
First, you need to start with the cover page. Here you enter basic information about your company, for example your Scope ID* and DUNS number**.
* You will receive your SCOPE ID once you have registered on the ENX platform.
**You can obtain your DUNS number via this link.
Maturity level and definitions
Next, we can start explaining how to work through the sections. Each section contains different questions. You need to answer these questions according to your company's maturity level, so you need to know what is meant by maturity level.
The maturity level is explained in the maturity levels of the catalogue. According to the VDA, there are six maturity levels from 0 to 5:
- Incomplete
- Performed
- Managed
- Established
- Predictable
- Optimizing
It is also advisable to read the definitions before you move on to answering the questions. This will give you a good understanding of the logic of the VDA ISA catalogue.
Information security
Each section contains several questions to determine your maturity level. The information security area is divided into different categories. As a result of your assessment, you will be rated in these categories:
- Information Security Policies and Organisation
- Human Resources
- Physical Security
- Identity and Access Management
- IT Security/Cyber Security
- Supplier Relationships
- Compliance
Prototype protection and data protection are separate modules that are only assessed for the corresponding labels.
How do I define my maturity level during the self-assessment for TISAX®?
To determine your maturity level, you first need to pay attention to the “must” and “should” requirements of the control questions. If you want to improve your maturity level, these requirements need to be in place. Naturally, your maturity level depends on the extent to which you have fulfilled these requirements.
As there are many control questions, each with several requirements, it is advisable to take some time for the assessment. It is worth investing in understanding the criteria so that you can have a smooth audit in the future. We therefore strongly recommend carrying out the self-assessment at the start of the project.
Finally, in the reference documentation column you enter where the evidence is located. This column can be filled in by providing the link to the reference documentation in your ISMS system. Alternatively, you can enter the name of the documented file in the corresponding control question.
You can obtain the current VDA ISA catalogue (ISA 6; for assessments commissioned from 1 January 2027, ISA 2027) from the ENX download area.
What are the success criteria of the self-assessment for TISAX®?
The target maturity level for every relevant control is level 3. The audit provider rates every control below that as a minor or major non-conformity. Major non-conformities must be remedied within nine months of the closing meeting; with minor ones, a temporary label is possible.
That is why it is important to carry out a self-assessment for TISAX® before you set your assessment date. Not only will you see where your potential for improvement lies – you can also put together a contingency plan to make sure you are ready for your audit.
If the self-assessment shows more gaps than expected, the TISAX® gap analysis is the structured next step — with a prioritized action plan.
Finally, the self-assessment for TISAX® provides a good benchmark in case your company prioritizes one of the categories mentioned above. Of course, there is always room for improvement.
What does the self-assessment for TISAX® cost?
Before we talk about the cost of the self-assessment for TISAX®, we would like to give you a rough idea of the overall costs. Here is a cost breakdown you can use:
- ENX registration €405 per location and scope (as of October 2026)
- Assessment fees of the audit provider as quoted by the audit provider (depending on the assessment level, billed directly)
- Consulting on TISAX® (expert team for preparation through to the assessment): AL2 from €18,000, AL3 from €24,000 (fixed price after scoping)
The prices above are approximate figures based on our experience in the market. Costs can vary depending on the number of locations, the existing infrastructure and your TISAX® maturity level (i.e. the result of your self-assessment for TISAX®).
Final thoughts
Preparing for your TISAX® audit is a lengthy, time-consuming process. It also requires hard work. However, the benefits of the TISAX® label outweigh the effort. It is therefore advisable to bring an expert on board right from the start.
Alternatively, you can book a workshop with us to define your roadmap for TISAX®. Do you have any further questions? Please contact us!
About the Author
Can Adigüzel is co-founder and managing director of 360 Digitale Transformation GmbH, a consultant for TISAX® and an ISO 27001 Lead Auditor with more than 200 audits. He has worked in IT project management since 2012 and in information security since 2019. He helps mid-sized companies implement information security pragmatically.