
What is a penetration test – and why does it concern your company too?
A penetration test – often simply called a “pentest” – is a targeted, controlled attack simulation. It examines how vulnerable your systems really are – not in a lab, but under realistic conditions.
Unlike conventional security checks, a penetration test goes into depth: professional testers take on the role of hackers and search for vulnerabilities that could be exploited from outside, from inside or through human error.
The goal? Not just to identify risks, but to show concretely how they could play out – before a real hacker does.
“We often see companies only truly understand how important a pentest is after an incident”, says Can Adigüzel, Managing Director of 360 Digitale Transformation GmbH. “In several cases, for example, we were able to obtain domain administrator rights – completely unnoticed. Scenarios like these show why prevention is a matter for top management today.”
Penetration test or vulnerability scan – what is the difference?
Both methods have their place in a security concept. But they are not the same thing.
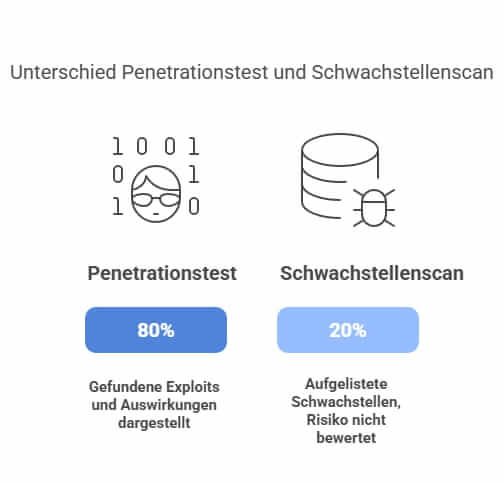
A vulnerability scan is an automated system check. It lists known security gaps with a generic rating (e.g. CVSS) – but without saying whether and how they can actually be exploited in your environment.
A penetration test, on the other hand, shows which of these vulnerabilities can actually be exploited – with what effort, what consequences and by which route. It combines technical analysis with human creativity.
Bottom line: A scan shows possibilities – a test shows reality.
Why are penetration tests more than a “nice-to-have” for ISO 27001?
ISO/IEC 27001:2022 does not explicitly require penetration tests. They are, however, a recognized means of meeting the requirements for the management of technical vulnerabilities (Annex A 8.8) and for security testing (A 8.29) and of demonstrating the effectiveness of your controls.
The standard requires you to monitor and evaluate the effectiveness of your security controls (clause 9.1). And this is exactly what an attack test delivers – traceable, documented and audit-ready.
Especially in industry, where connected machines, sensitive production data and external interfaces come together, such tests are a central part of risk assessment. And clear proof to auditors, customers and partners:
“We know our risks – and we act on them.”
Why are penetration tests indispensable for industry today?
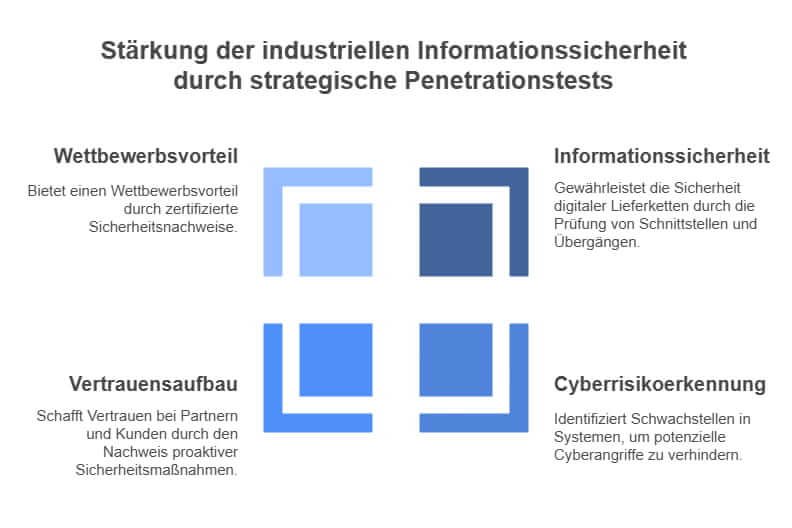
Ensuring information security in digital supply chains
As industrial processes become increasingly digitalized, the dependencies within your supply chain grow as well. Systems, data flows and maintenance access are now often closely interconnected with partners and service providers.
But what happens if a weak point lies not in your company, but with one of your external partners?
A penetration test helps you systematically examine exactly these interfaces and transitions. Remote access, industrial control systems (ICS) and IoT components in particular are frequent targets – and potential entry points for cyberattacks.
A well-founded test lets you identify these risks early – and strengthen the digital resilience of your entire supply chain.
Identifying cyber risks before they cause damage
Whether ransomware, industrial espionage or sabotage – cyberattacks on industrial companies aimed at penetrating their systems are no longer the exception. The question is no longer whether you will be affected – but whether you are prepared.
A penetration test shows you where your systems are really vulnerable. Not on paper, but in a real scenario: through attacks on computer networks, networks, web applications or user accounts – simulated under controlled conditions.
This gives you not only a list of priorities, but concrete recommendations for action to eliminate vulnerabilities in a targeted way – before they turn into security incidents.
Building trust – for audits, customers and partners
Reliable security structures are a decisive trust factor today. Business partners, customers and certification bodies do not just want to see processes – they want clear evidence of security in practice.
An up-to-date security evaluation is exactly that: tangible proof that you act proactively and take risks seriously.
Particularly in the context of an ISO 27001 audit or in tenders, a documented test report is a plus point that builds trust – internally and externally.
Competitive advantages through documented security evidence
IT security has long been more than an internal IT topic – it is becoming a business-relevant differentiator.
A completed penetration test is not just technical evidence, but often a decisive factor when customers and clients choose a supplier. Especially when they are subject to strict compliance requirements.
Combined with your ISO 27001 certification, the test shows:
“We know what we are doing – and we let ourselves be measured.”
Which types of penetration tests suit your company?
Black box, white box or gray box – the test types compared
Not every attack test is the same. Choosing the right test method depends on which systems are to be tested – and which level of information you want to simulate.
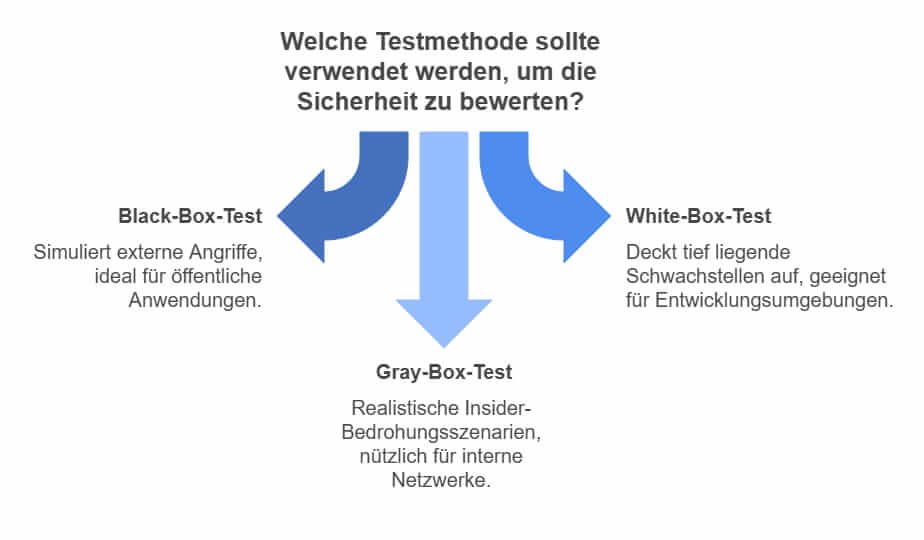
- In a black-box test, the tester receives no prior knowledge of your infrastructure. This method mimics the typical attack of an external hacker. It is particularly suitable if you want to know how your company looks from the outside – for example for public web applications or internet access points.
- A white-box test is carried out with full access to documentation, source code or system configurations. This approach also uncovers deep-lying vulnerabilities that would be hard for hackers to reach – ideal for the security assessment of development environments or critical systems.
- The gray-box test lies in between: the tester knows basic information such as user roles or internal structures – just like an insider with limited access. This variant is particularly suitable for realistic threat scenarios within the corporate network.
Which approach makes sense for you depends on your objectives and the system area to be tested.
Special forms: social engineering, physical and wireless attacks
In addition to classic IT scenarios, there are also test methods that target the human factor or the physical infrastructure:
- Social engineering tests (e.g. a phishing simulation (in German)) check whether employees respond to phishing e-mails, disclose passwords or unintentionally pass on sensitive information. This makes it possible to identify awareness gaps and close them in a targeted way.
- Physical penetration tests simulate attempts to gain access to secured areas – for example through tailgating or manipulated visitor badges. An important method, especially in companies with production facilities or on-site server rooms.
Wireless penetration tests focus on Wi-Fi networks, Bluetooth devices or IoT radio protocols. These tests show whether wireless interfaces can be compromised unnoticed – an often underestimated risk factor.
Application-specific tests: web applications, networks & more
Modern industrial companies use a wide range of systems – from customer web portals and internal databases to connected machine controls. Penetration tests must be just as varied.
- A web application penetration test focuses on the security of the frontend, backend and interfaces (APIs) – including injection attacks, cross-site scripting or insecure authentication (in line with the OWASP Top 10).
- Network-based penetration tests check whether unauthorized access or privilege escalation is possible in the internal or external network – typically via open ports, outdated services or faulty segmentation.
- Cloud environments, mobile apps or SCADA/ICS systems can also be tested specifically today – taking industry-specific standards and technical particularities into account.
The goal is always the same: clarity about which systems are vulnerable and how – and which protective measures actually work.
How professional penetration testing works
A successful security evaluation follows a structured process – methodically sound, documented and tailored to your individual IT landscape. The aim is not only to identify vulnerabilities, but to assess how exploitable they actually are – and to derive concrete protective measures from this.
Get to know our penetration testing service.
Planning & defining objectives: what is tested and why?
The first step is a precise definition of objectives: which systems are to be tested? Is it about external servers, internal network security, web software or mobile solutions? Will a black-box or a gray-box test be carried out? Who receives which information?
Together with the penetration tester, you define the test objectives, test scope and security boundaries. This ensures that the test is realistic, legally sound and aligned with your security objectives.
Reconnaissance: how attackers gather information
In the reconnaissance phase – also known as “footprinting” – the tester collects all publicly available information that could be used for an attack. This includes DNS records, metadata, open ports, outdated services or even sensitive data on social networks.
This step simulates exactly how a real attacker proceeds to get a picture of the target system – and to identify the first attack vectors.
Vulnerability analysis & exploitation: uncovering security gaps
Now the actual core of the test begins: the search for concretely exploitable vulnerabilities.
Using tools such as Nmap, Burp Suite or Metasploit, the tester scans specifically for weaknesses – such as insecure authentication, misconfigured firewalls or unpatched system components.
Where possible, these vulnerabilities are then exploited in a controlled manner – always within the agreed test parameters. The aim is to make the actual impact visible, e.g. through access to sensitive data or escalation of user privileges.
Pentest reporting & measures: what you can learn from the test
At the end of the test there is a detailed report with all findings, ratings and recommendations. Each identified vulnerability is classified by criticality (e.g. CVSS score) – supplemented by screenshots, exploit examples and technical background information.
Particularly valuable: you receive practical recommendations for action, tailored to your IT environment and your internal processes.
The report is also suitable as evidence in ISO 27001 audits – it shows that you identify, assess and actively address risks.
Good to know:
A good report is not just a look back, but also a roadmap for your next security measures.
Pentest follow-up & continuous improvement: stay vigilant
A penetration test is not a one-off project – but a building block of a continuous security process. The identified vulnerabilities should be remediated and documented promptly. After that, a retest is often advisable to verify the effectiveness of the measures.
Regular, targeted tests – for example after system changes, software updates or new interfaces – also help you strengthen your company's security for the long term.
Because: threats evolve – and so should your defenses.
Good to know:
Security is not a state, but a process. Regular tests help you stay one step ahead.
Standards, tools and best practices in use
OWASP Top 10, NIST SP 800-115 and their importance for penetration testers
Professional penetration tests are not based on gut feeling, but on internationally recognized standards and test frameworks. These ensure comparability, traceability and quality – a key aspect, especially if you also want to use the results for ISO 27001 audits.
The OWASP Top 10 (current edition: 2025) describe the ten most critical risk categories for web applications – such as injection attacks, insecure authentication or misconfigured access controls. A must for all tests in the web environment.
The NIST SP 800-115 framework describes a structured approach to security testing and serves many penetration testers as a methodological foundation – from scoping through test execution to reporting.
Your advantage: A test according to these standards provides not only technical insights, but also audit robustness and reliability.
Which tools do professional pentesters work with?
Penetration testers use a combination of open-source tools, commercial solutions and their own scripts to track down vulnerabilities and simulate attack scenarios realistically. Here is an overview of common tools:
- Nmap: network scanner for detecting open ports and services
- Burp Suite: analysis and manipulation tool for web applications
- Metasploit: framework for the automated exploitation of known vulnerabilities
- Nessus: vulnerability scanner for assessing system hardening
- Wireshark: network protocol analysis for traffic inspection
Professional testers combine these penetration testing tools with experience and creativity in order not only to find known vulnerabilities, but also to uncover complex attack paths that automated scanners often miss.
External vs. internal tests: which makes more sense?
Many companies ask themselves this question – especially when it comes to efficiency, confidentiality and use of resources.
An external penetration test examines your systems from the perspective of a real attacker – that is, without internal knowledge. Ideal for assessing the “attack surface from outside” – e.g. public servers, web portals or VPN access.
An internal test, by contrast, simulates attacks from within the corporate network – for example via compromised endpoints, insufficiently protected user accounts or faulty assignment of privileges. It is particularly useful if you want to assess the impact of an insider attack or an infected device.
Tip: In many cases, combining both perspectives – an external and an internal test in one project – is the most efficient and realistic way to examine your systems holistically.
Answers to typical questions from 360DT's practice
How often does a penetration test make sense?
The answer depends heavily on your IT landscape and your risk profile. As a rule of thumb:
At least once a year – or whenever significant changes occur:
- Introduction of new systems or applications
- Migrations to the cloud
- Changes to access rights or network infrastructure
- Integration of new partners or service providers
- Before or as part of an ISO 27001 audit
Tip: Plan penetration tests as a recurring part of your information security management system (ISMS) – this way you avoid surprises and continuously strengthen your security level.
What prerequisites must be met internally?
A successful test does not require perfect IT – but a few basic points should be clarified internally:
- Clear definition of objectives: Which systems are to be tested?
- Contact persons: Who is available for questions, and who approves technical access?
- Legal safeguards: Is there approval from management and, where applicable, the works council?
- IT availability: Depending on its depth, the test may cause temporary system load – your IT should be informed and prepared.
Good to know:
A reputable provider supports you in preparing the test and coordinates all parties involved so that the process runs smoothly and on a sound legal footing.
What does a good penetration test cost – and what does not having one cost?
The costs depend on the scope, complexity and test method. For small, clearly defined web applications, our tests start from €3,600 (fixed price after scoping). Extensive tests of entire networks or infrastructures can be considerably higher.
But the more important question is:
What does it cost if a penetration test is not carried out?
- A successful cyberattack can paralyze systems
- Production downtime, reputational damage and fines are a real threat
- ISO 27001 audits could fail
- Customers and partners could lose trust
A penetration test is not just an expense – but an investment in your security, your ability to get certified and your future viability.
About the Author
Can Adigüzel is co-founder and managing director of 360 Digitale Transformation GmbH, a consultant for TISAX® and ISO 27001 Lead Auditor with more than 200 audits. He has worked in IT project management since 2012 and in information security since 2019. He helps SMEs implement information security pragmatically.