
- 360 DIGITALE TRANSFORMATION
External CISO: The Security Your Organization Needs – Flexible and Cost-Efficient
An external CISO – also called vCISO or virtual CISO – gives your organization the information security leadership of an experienced Chief Information Security Officer, without the fixed costs of an internal full-time position. As your central point of contact, we take care of ISO 27001, TISAX® and NIS-2 (in German) – flexibly, practically and tailored to your budget.
Are You Facing These Challenges?
Identify the security gaps in your organization and find out how the vCISO can help you.
Lack of In-House Expertise in Information Security
Your IT department may not be sufficiently equipped to meet the growing demands on information security? A specialized CISO could be the solution to close gaps and take your security strategy to the next level.
Complexity of ISO 27001 Implementation
The requirements of ISO 27001 are extensive and can seem overwhelming. You need to make sure that all IT security standards are met without disrupting the day-to-day operations of your organization. Our virtual CISO service helps you make the entire process understandable and efficient while keeping an eye on your budget. An external vCISO also supports an ISMS according to VDA ISA (TISAX®) or the implementation of NIS-2 obligations under the BSI Act (BSIG). Under NIS-2, management remains responsible (Sec. 38 BSIG) – the vCISO prepares decisions and delivers the legally required training for management.
Need for Cost-Efficient Security Consulting Without a Full-Time Position
You need sound security expertise but do not want to carry the fixed costs of a full-time position? An external CISO delivers exactly the competence you need – scalable and at a predictable monthly fee.
If the focus is less on strategy and more on the operational running of the ISMS, the external information security officer (in German) is the more suitable model.
Our External Chief Information Security Officer (CISO) for Your Information Security
Find out how our vCISO service strengthens your information security and supports your ISO 27001 certification.
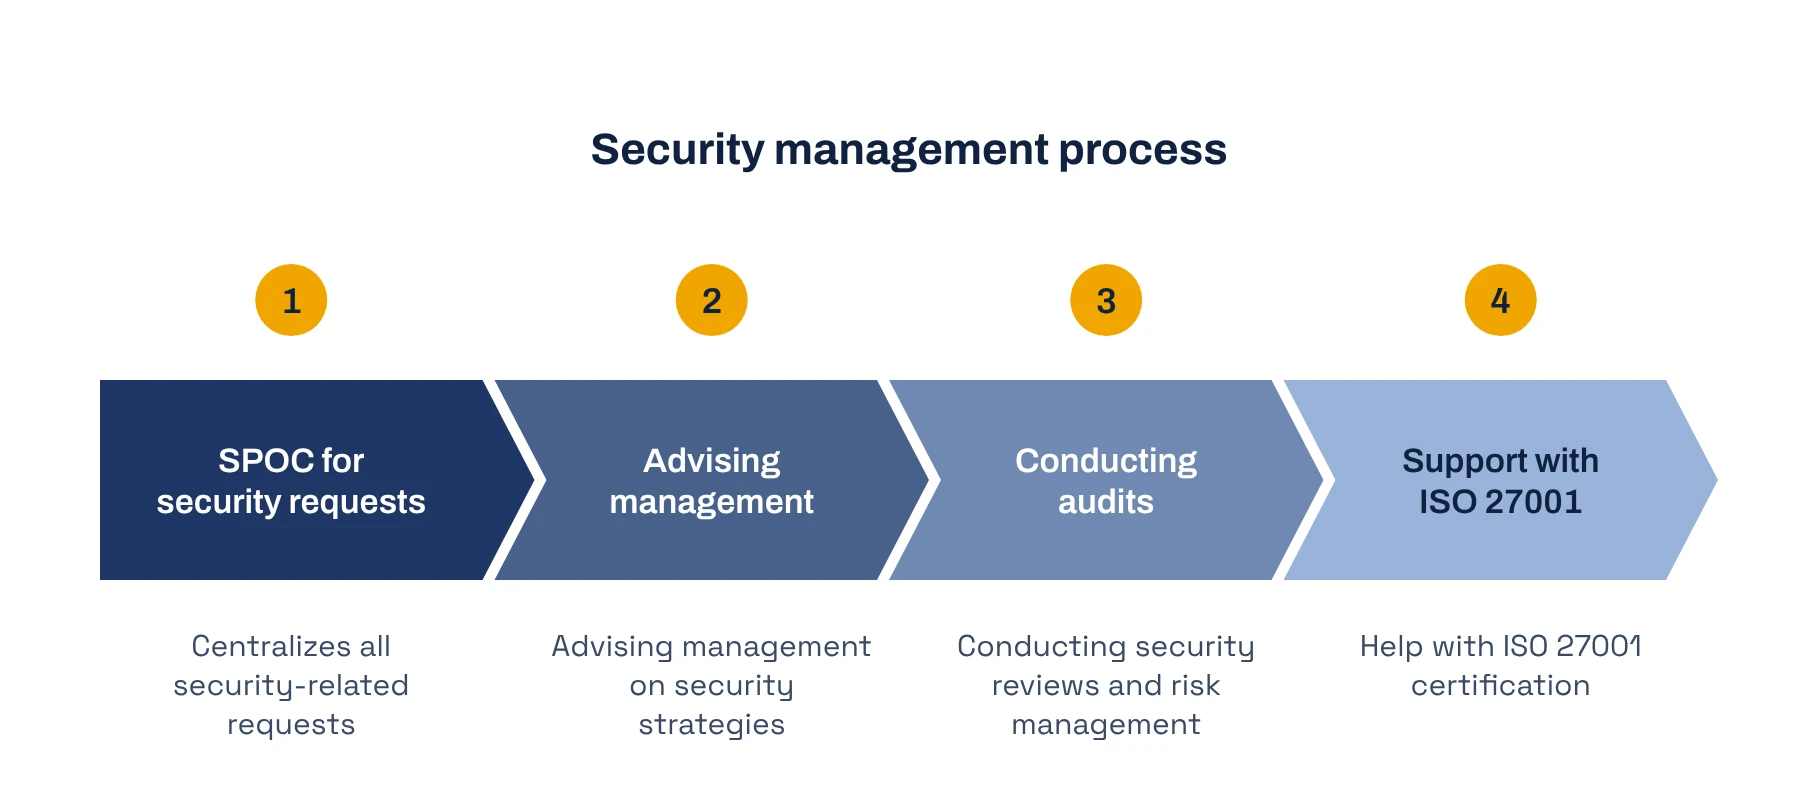
SPOC for All Security Requests
As your single point of contact (SPOC), we are your central contact for all questions relating to information security, cyber security and compliance. Whether internal or external requests – we coordinate everything and make sure your organization is optimally protected at all times.
Advising Management on All Security Matters
Our vCISO supports management at all levels by making strategic recommendations for improving your security architecture. We help you identify security risks and develop a sound, forward-looking security strategy.
Proactive Audits and Risk Management
We plan and organize regular internal audits and risk management reviews – the audits themselves are carried out by an independent auditor from our team who is not involved in your ISMS. This way, you avoid potential weaknesses and protect yourself against future risks.
Support With ISO 27001 Certification
From the gap analysis to a successful audit, our vCISO guides you through ISO 27001 certification, preparation for the TISAX® assessment or the implementation of NIS-2 obligations. We make sure that your organization meets all relevant requirements and that your certification runs smoothly, while offering continuous monitoring.
How Working With an External CISO Works
A clear process for implementing your virtual CISO, tailored to your organization.
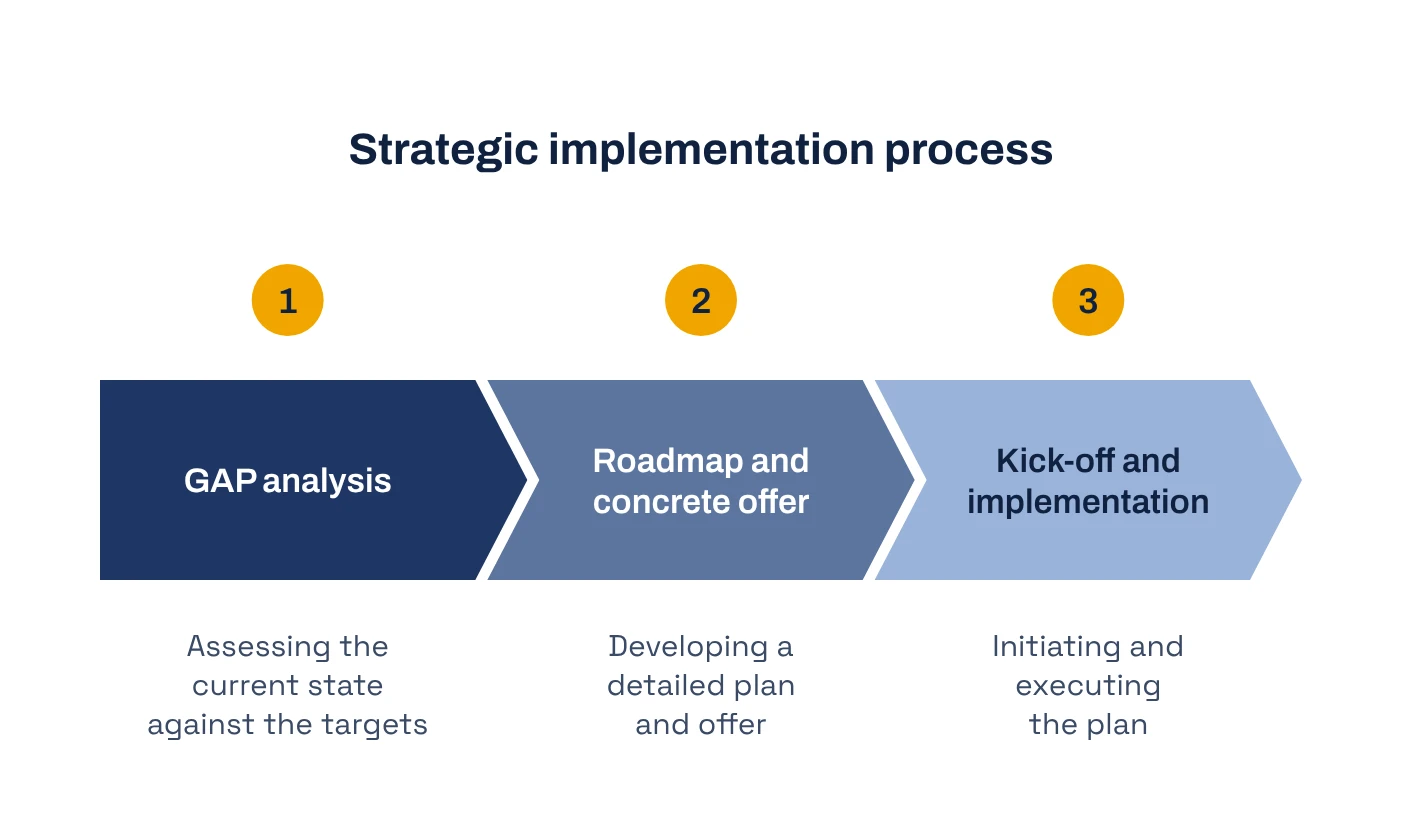
GAP Analysis – Understand Your Current Security Gaps
We start by jointly analyzing the current state of your information security. Through a detailed GAP analysis, we identify weaknesses that may expose your organization to security risks. We gain a comprehensive overview to understand exactly where your requirements lie and which security gaps need to be closed.
Roadmap and Concrete Offer – Based on the Results of the GAP Analysis
After the analysis, we create a tailored roadmap that sets out the route for implementing your security measures. On this basis, we provide you with a transparent offer adapted to your needs – so you always have a clear view of costs and services.
Kick-Off and Implementation – Start With a Clear Plan and Efficient Execution
Once you have accepted the offer, we start implementation quickly and efficiently. In a kick-off meeting, we finalize the plan and implement it in close cooperation with your team. Our goal: your security measures are seamlessly integrated into your operations and your ISO 27001 certification is achieved efficiently.
How We Work — the Control Plan From Our Practice
54 controls with a fixed cycle, clear evidence and responsibilities. This is exactly the tool we use when we take on the role at your organization.
You will receive the download link by e-mail within a few minutes.
Our Skills – Your Outsourcing Advantage
Benefit from our expertise in ISO 27001, TISAX® and NIS-2.
Consulting by ISO 27001 Lead Auditors
Our team consists of experienced ISO 27001 Lead Auditors with sound knowledge and extensive experience in implementing and auditing information security management systems (ISMS). We make sure that your security processes meet the requirements of ISO 27001. Our consultants on TISAX® support you in the automotive industry.
Experience Implementing Security Solutions for Mid-Sized Industrial Companies
We have extensive experience in advising on and implementing security solutions specifically for mid-sized industrial companies. Our approach is practice-oriented and tailored to the particular needs of your industry. We understand the challenges that organizations like yours face and offer tailored solutions that integrate seamlessly into your processes.
Support in Maintaining ISO 27001 Certification
ISO 27001 certification is an ongoing process that requires regular audits and continuous adaptation to new security requirements. Our vCISO service supports you not only with initial certification, but also with the long-term maintenance and improvement of your ISMS. We make sure that your certification always stays current and that your organization is always up to date with security requirements.
Client Experience: How Our CISOs Have Made Organizations More Secure
Tier 2 Supplier: TISAX® Label in Six Months
With our vCISO service, a Tier 2 automotive supplier passed the TISAX® assessment without deviations within six months and obtained the TISAX® label. Through continuous process optimization, risk management workshops and structured hands-on consulting, the level of information security was improved sustainably. Our vCISO took over ISMS administration, audit preparation and management meetings, so that the organization met the requirements efficiently and without stress.
What Our External CISOs Cost
You do not pay by the hour. Each package is a fixed monthly fee – consulting, coordination and the services listed in the package are included, without timesheets. You can choose between the Bronze, Silver and Gold packages and the individual Platinum package. We clarify which package fits in the free initial call.
Bronze
Consulting
from €1,200/month
For organizations with their own information security officer or IT team
- SPOC for security questions
- Management consulting
- Guidance on ISO 27001 · TISAX® · NIS-2
- Support for the management review
Fixed monthly fee · 12-month term · billed annually
Silver
+ Steering
from €1,550/month
For ISMS implementation and recertification
- Everything in Bronze
- ISMS project steering
- Measures, deadlines & owners
- Reporting to management
Fixed monthly fee · 12-month term · billed semi-annually
Gold
+ Hands-on
from €2,250/month
For organizations without internal capacity
- Everything in Silver
- Implementation & documentation
- Audit preparation
- Support during the certification audit and TISAX® assessment
Fixed monthly fee · 12-month term · billed quarterly
Platinum
Enterprise
Price after scoping
For multiple sites and groups
- Everything in Gold
- Multiple sites / group
- SLA & prioritized availability
- Dedicated vCISO
- Regular jour fixe & steering committee
- Deputy cover – continuity
- On-site presence
Term & billing individually agreed
Find the right package – free initial call
One call for all packages – we recommend the right one for you.
All prices are net plus VAT. Travel costs for appointments outside Berlin are charged at cost. From approximately 200 employees, we prepare an individual offer.
Start Optimizing Your Information Security Today
Benefit from tailored IT security with our vCISO – flexible and cost-efficient!